Stop attackers at the door
CrowdSec now blocks the addresses that attack your web applications, and Tenkai tells you when a server lets in someone it did not.
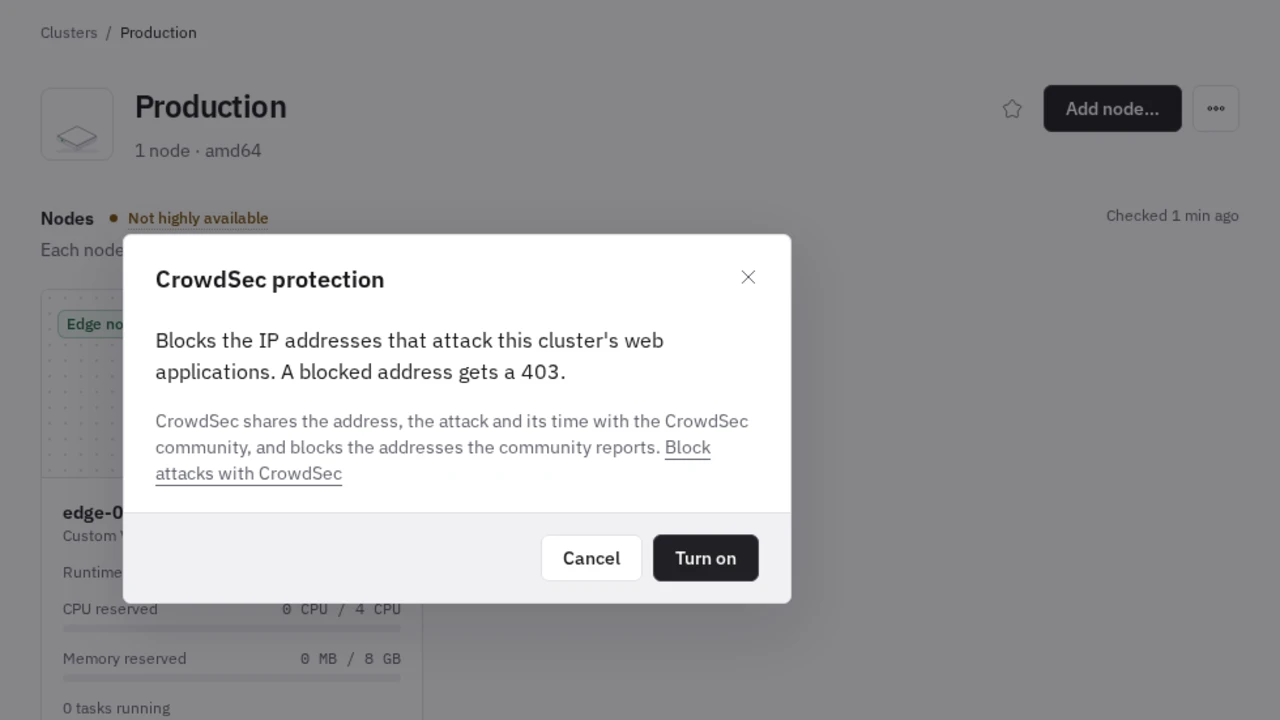
Your servers face the internet all day. Tenkai now blocks the attacks it can, and tells you about the doors it did not open.
Block attacks with CrowdSec
In the cluster menu, CrowdSec protection… turns it on. The edge node then blocks the addresses that scan for admin pages, brute-force logins or look for known flaws, and the addresses the CrowdSec community reports. A blocked address gets a 403 from every web application of the cluster.
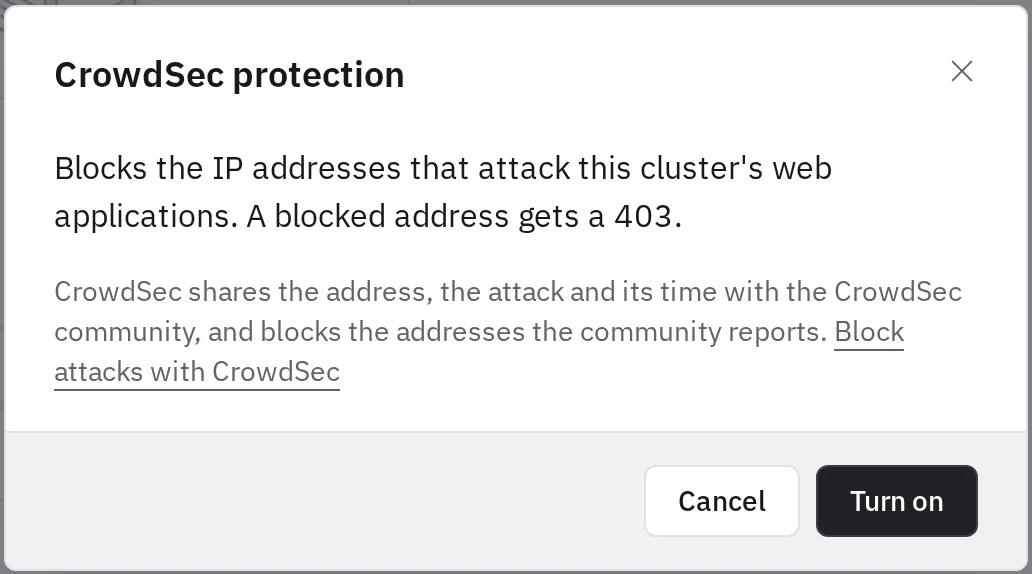
CrowdSec shares the address, the attack and its time with its community, never the requests. It comes with every paid plan, and you can give it to each new cluster from your team settings.
See Block attacks with CrowdSec for the details.
See the SSH keys Tenkai did not add
SSH access in the SSH tab of a server now shows every key that can log in and that Tenkai did not add, in red when it appeared after the first check. A new one also shows in health.
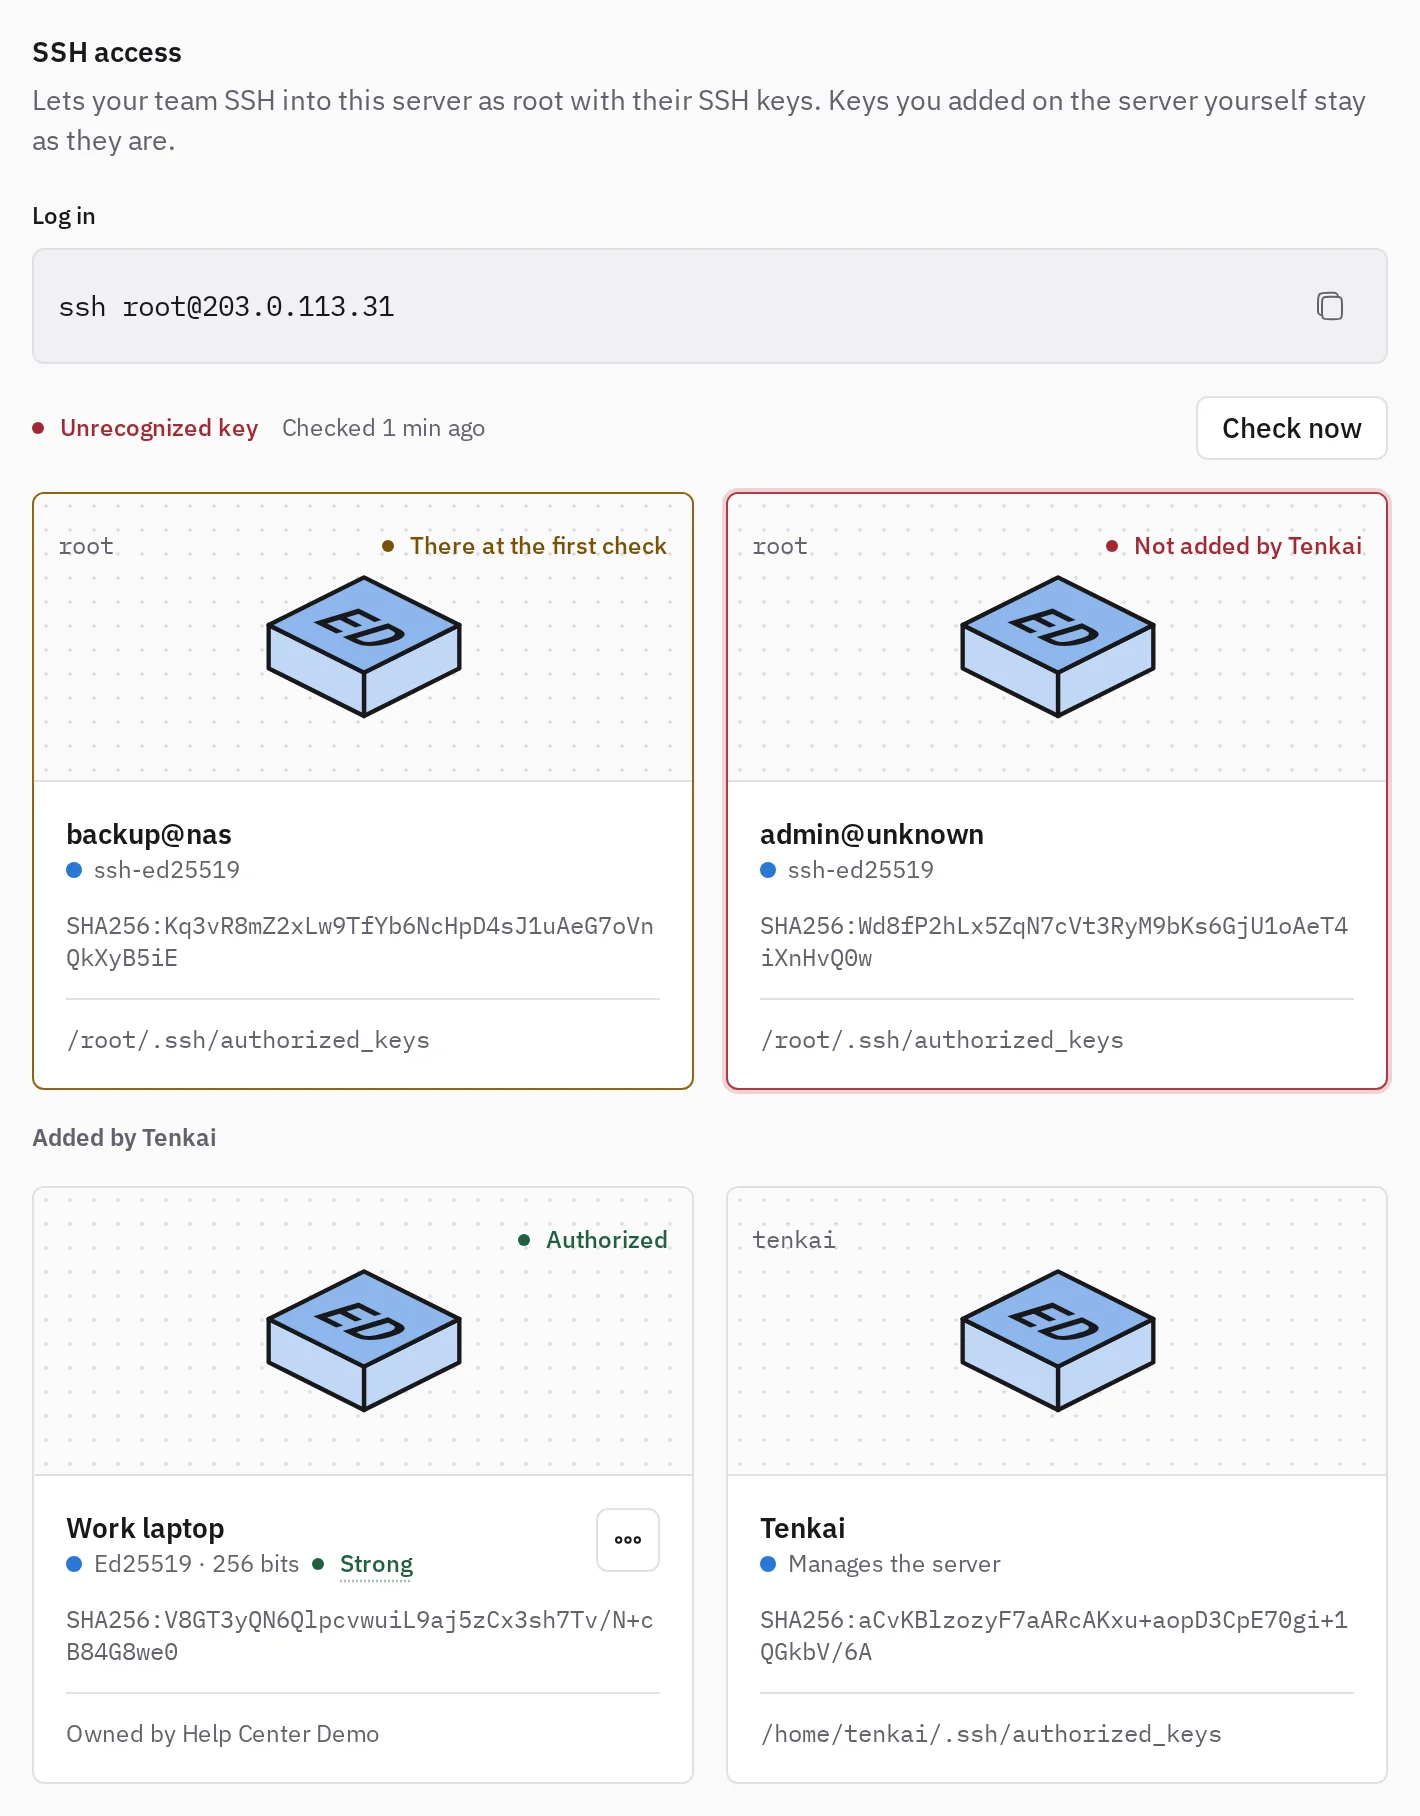
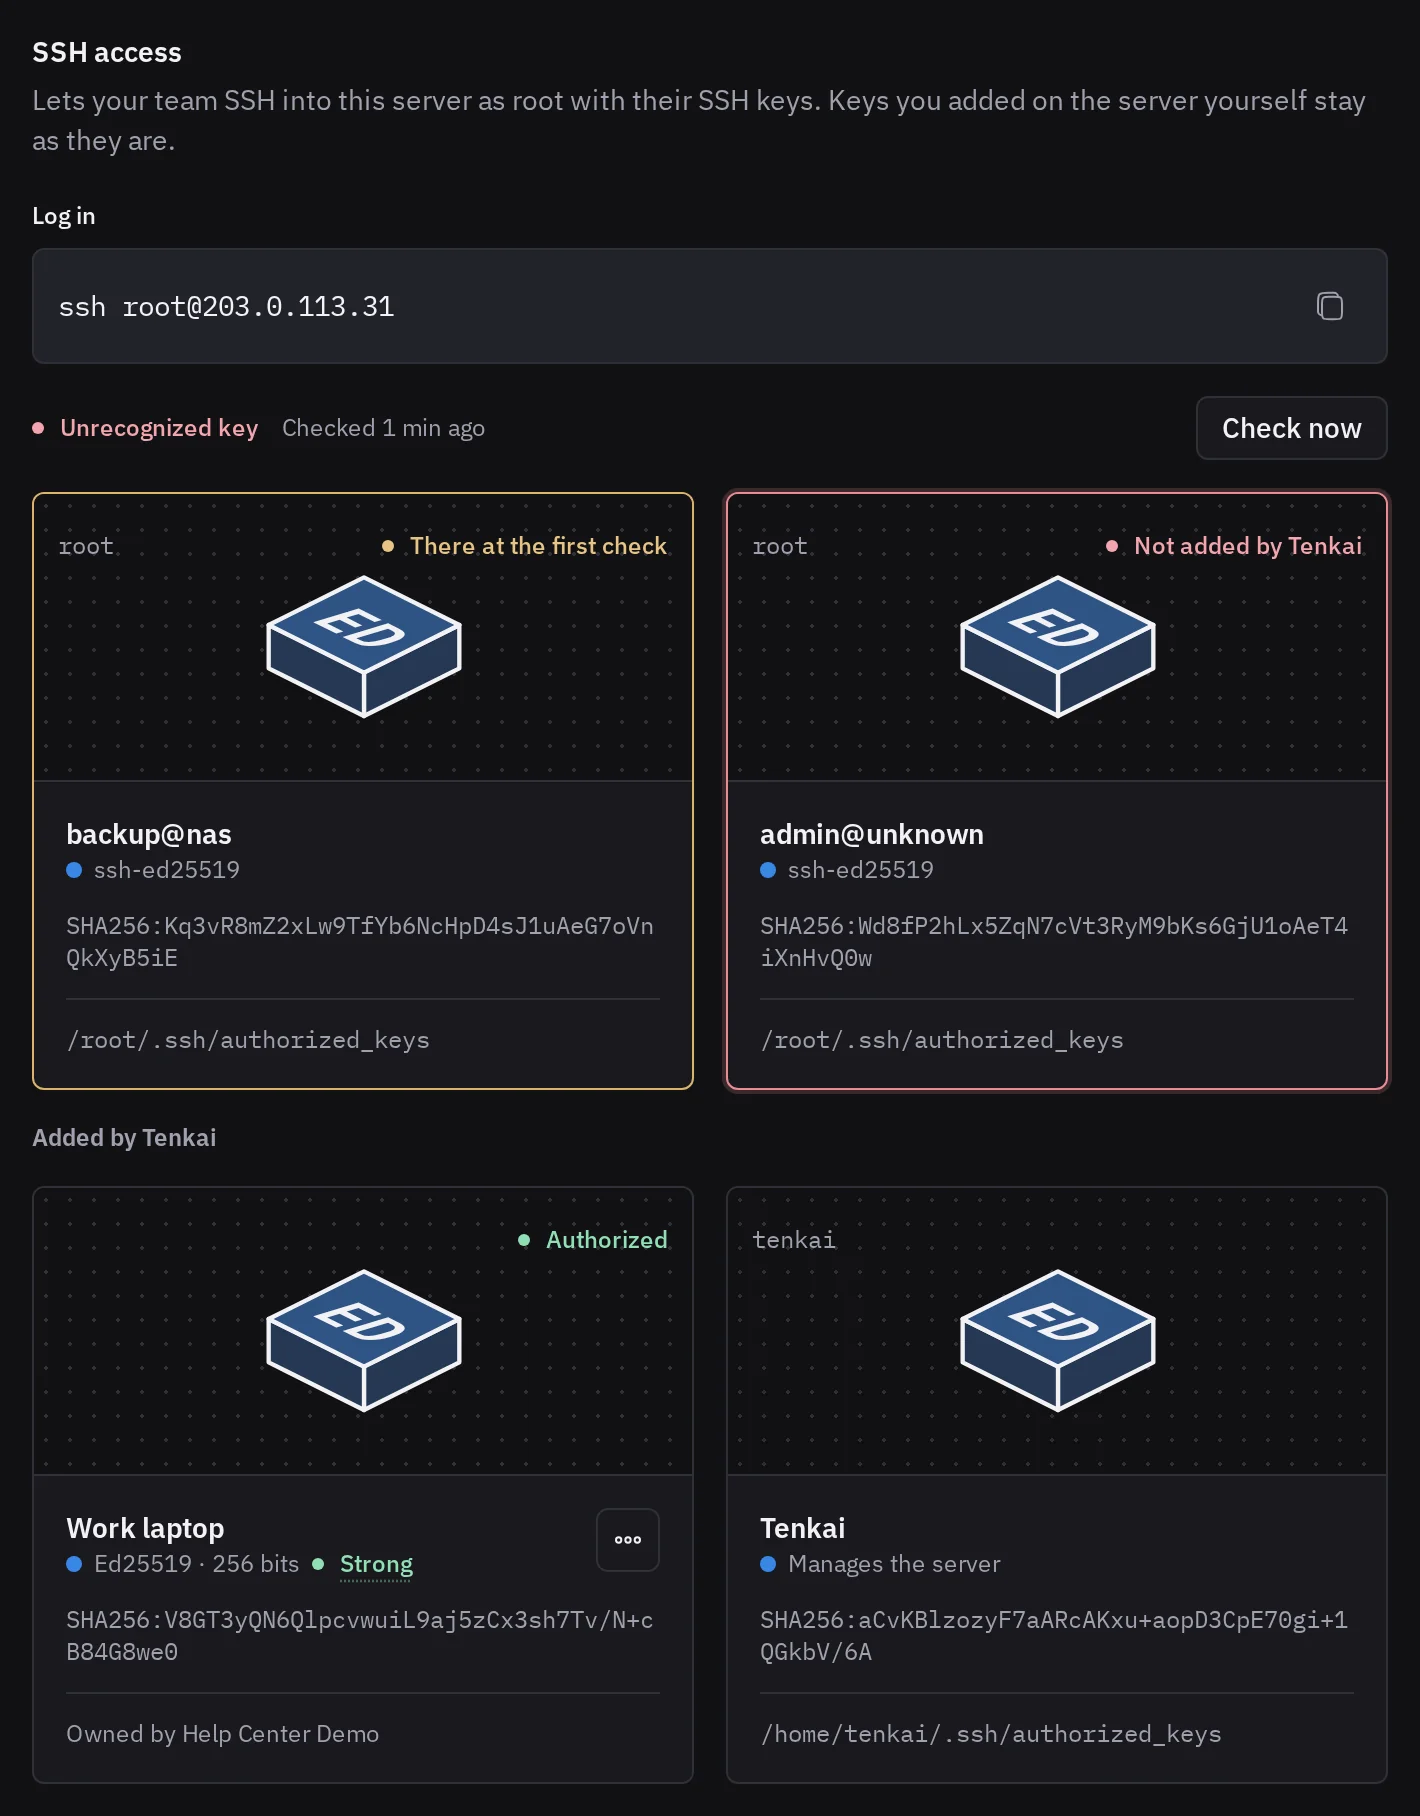
See who can log in for the details.
Find the ports left open
The Firewall tab of a server lists the ports that a ufw rule opens without Tenkai, and the processes outside Docker that ufw lets the internet reach. Close one, then choose Check now.
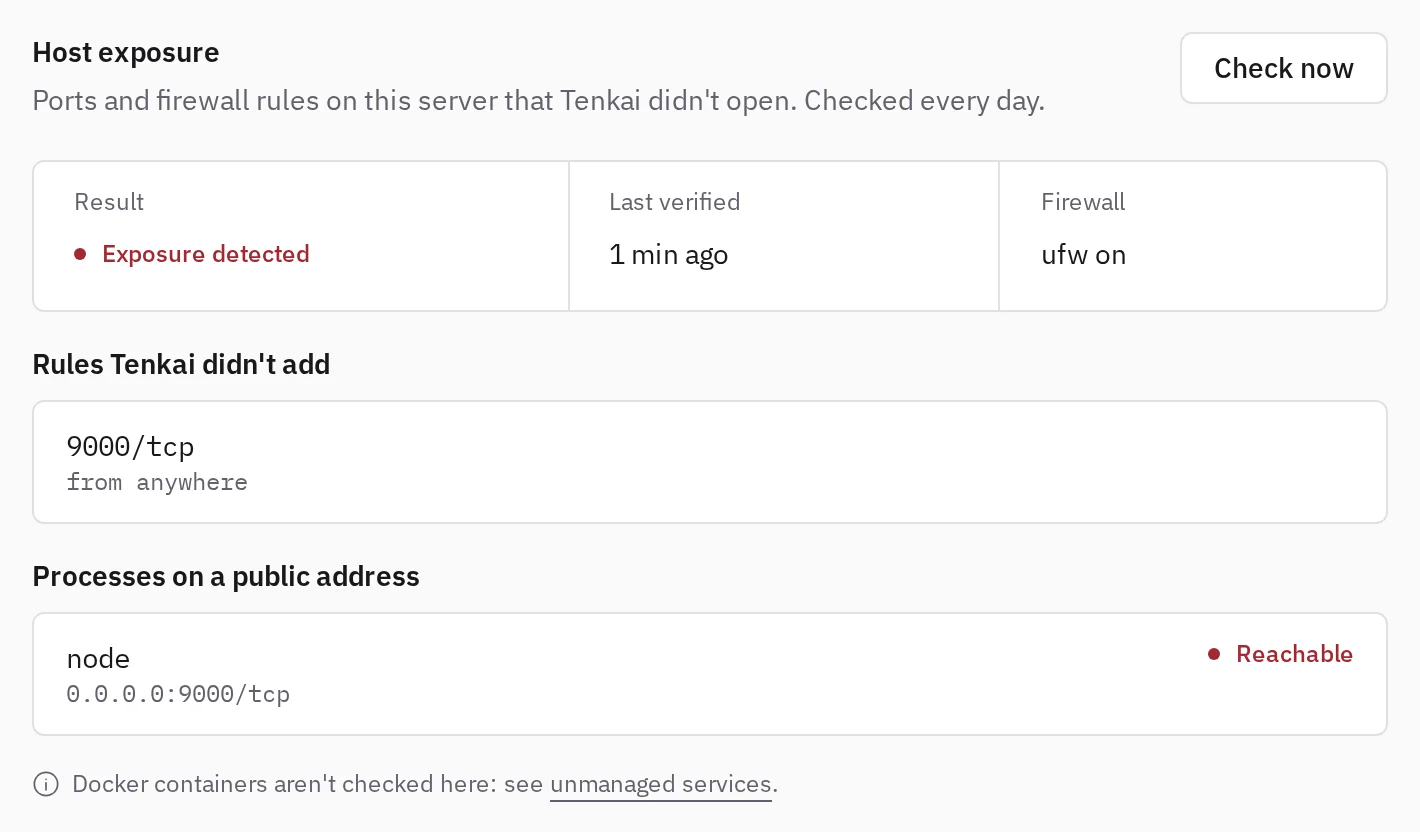
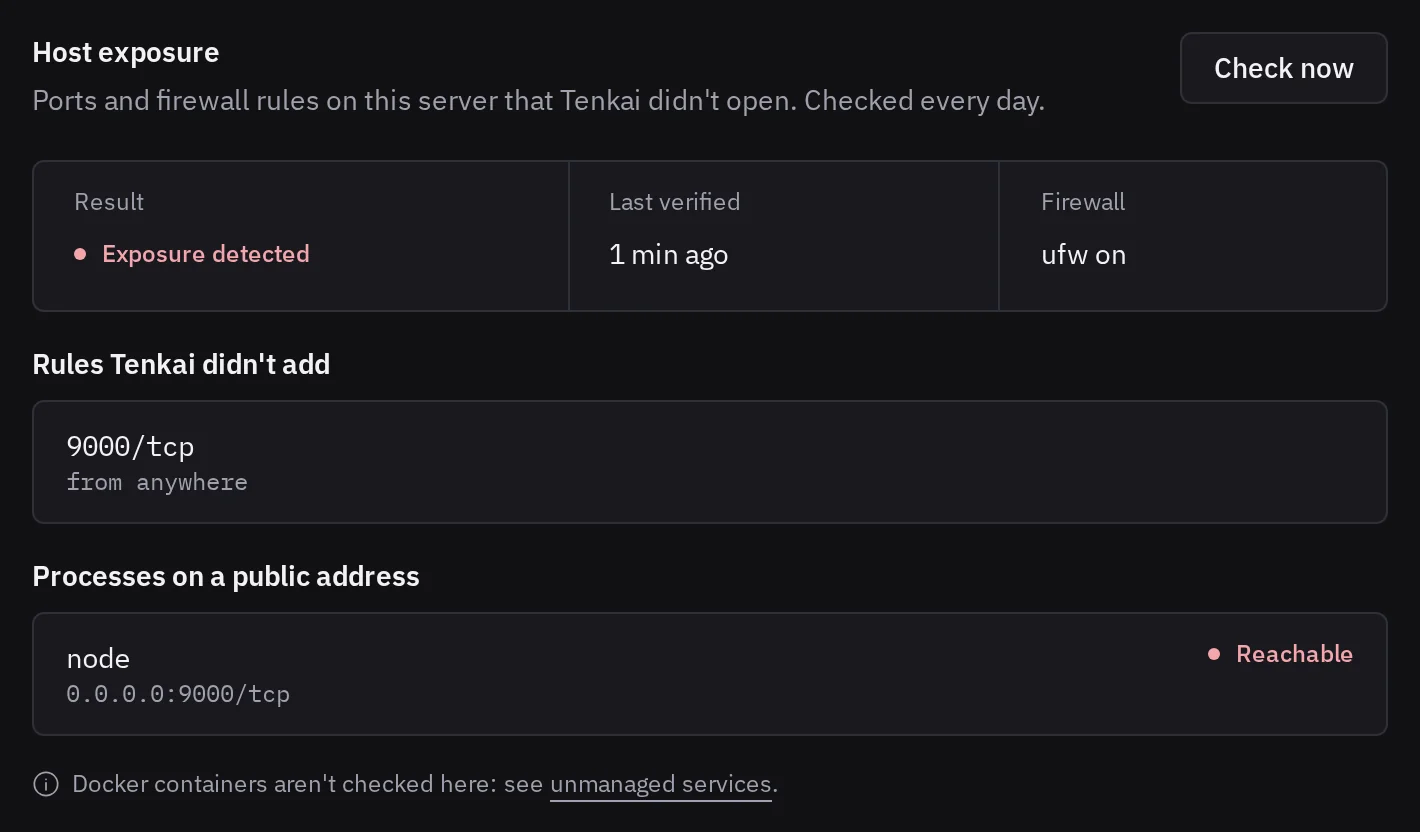
See Ports left open for the details.
Both checks run every day, on the Pro and Team plans.